For many digital forensics professionals, Android devices have represented the more accessible side of mobile forensics for years. While iPhone devices gradually gained a reputation as tightly controlled systems deeply integrated into Apple’s security ecosystem, Android was perceived as a more flexible platform that provided investigators with more room for technical analysis, research, and customization.
Such a perception did not emerge by accident. Numerous Android devices allowed bootloader unlocking, installation of custom recovery environments, and the use of development communication channels through USB interfaces. For advanced users, software developers, and security researchers, this did not only mean greater freedom of operation, but also the possibility of accessing parts of the system that were significantly more restricted on other platforms. [1][2]
For digital forensics professionals, this meant that, besides official acquisition methods, alternative technical paths often existed. Which of those paths could be applied depended on the device model, operating system version, and perhaps most importantly, the experience of the investigator.
Although encryption has never been unknown to the Android platform, the security model of earlier device generations relied on a different balance between flexibility and protection. The boundary between user access, service access, and investigative access was, in many cases, significantly less strict than it is today.
Over the last several years, this balance has almost completely changed. The change can perhaps best be seen directly in the forensic laboratory. In the past, the first question was which extraction method we would apply. Today, it is often more important what state the device is in, because that state may determine whether a technical path to the data exists at all.
When a modern Android flagship device arrives at a laboratory today, the first question is no longer only which extraction method we can apply, but what possibilities its current security state allows in the first place. Is the device unlocked? Was it rebooted after seizure? Are the cryptographic keys still available? The answers to these questions often have a greater impact on the course of the analysis than the device model itself.
This change represents one of the greatest turning points in mobile forensics since user data encryption became an integral part of the security architecture of modern smartphones. Today’s Android devices combine File-Based Encryption, hardware-protected cryptographic keys, and security mechanisms that connect system integrity with the ability to access data. [3][4]
Because of this, two seemingly identical devices no longer necessarily represent two identical forensic situations. A locked and an unlocked Samsung Galaxy S25 may have the same hardware, the same operating system version, and support from the same tools, yet provide completely different analytical possibilities. The difference is not in the device itself, but in the circumstances that exist before the analysis even begins.
This is the key change in modern Android forensics. Today’s devices are not only more secure, but they also make fundamentally different decisions about whom they will trust. Access to data is no longer a consequence of physical possession of the device, but rather a combination
of user authentication, system integrity, device security state, and availability of cryptographic keys. [3][4][5]
In other words, a modern smartphone no longer checks only who physically holds it. It simultaneously evaluates whether that environment meets the security requirements necessary to access the data. This change represents the starting point for understanding modern Android forensics.
Android As We Once Knew It
To understand the current state of Android forensics, it is necessary to look back several years and examine what the platform looked like before security became the dominant philosophy of development.
In the early and mid-2010s, Android was often described as an open ecosystem. Although this term was most commonly used in the context of application development, user interface customization, and system modification capabilities, that openness had very concrete consequences for digital forensics as well.
Many devices from that period offered capabilities that are difficult to imagine on modern flagship models. Bootloaders could often be unlocked relatively easily, custom recovery environments such as TWRP were widely used, and USB debugging represented an important communication channel between the device and a computer. These capabilities were not identical across all manufacturers or models, but they represented an important part of the Android ecosystem before security controls became significantly stricter. [1][2]
For digital forensics professionals, this meant that, in addition to official acquisition methods, there was often a range of alternative technical approaches. An investigator with deep knowledge of a specific device model could, depending on the circumstances, use service interfaces, recovery environments, or other advanced methods to achieve a level of access that is no longer common today.
However, it is important to emphasize that Android devices of that era were not simply “insecure.” The difference was not that security did not exist, but rather that the balance between security, flexibility, and customization possibilities was different. Manufacturers still dedicated significant attention to users who wanted to explore devices, develop their own software, or have greater control over the system.
This flexibility created an interesting situation for the forensic community. On one hand, devices represented a challenge because they required deep technical understanding of their architecture. On the other hand, an investigator who understood how a particular model worked often had more possibilities than would be possible today.
The situation began to change as smartphones stopped being merely communication devices and became the center of a user’s digital identity. A phone no longer contained only contacts, messages, and photos. It began to store business documents, financial applications, authentication tokens, access to cloud services, and a large part of the user’s everyday digital life.
At the same time, security risks changed as well. Attacks against mobile devices became more sophisticated, commercial spyware solutions capable of targeted surveillance appeared, and mobile platforms became valuable targets for criminal groups and advanced attackers. [6][7]
The industry therefore changed its priorities. The goal was no longer only to provide users with the greatest possible level of control over their devices, but to build a platform capable of protecting data even in situations where an attacker physically possesses the device. [3][4]
This is where the most important change for mobile forensics begins.
Android did not stop changing because openness was a wrong concept. The change occurred because devices became too valuable for security to depend only on software limitations within the operating system.
ingle technology. It developed gradually, through several phases in which Android transitioned from a platform that emphasized flexibility and customization into a system where security became a fundamental part of the entire device architecture.
For digital forensics, this change did not only mean the disappearance of certain access methods. The entire way of thinking about the device changed. While in the past technical knowledge about a specific device model could often open additional possibilities for analysis, today it is equally important to understand the security state of the device, the availability of keys, and the relationship between hardware, operating system, and user authentication.
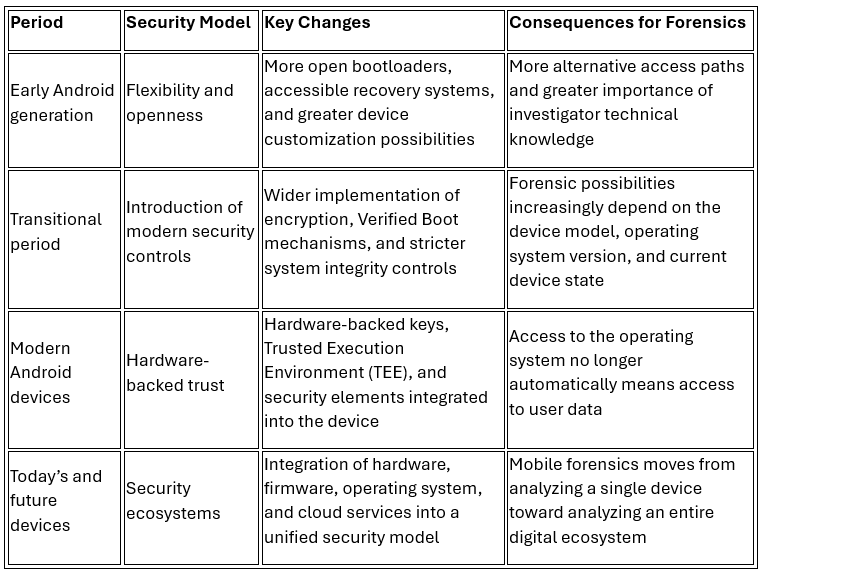
Note: These phases are not strictly tied to a specific Android version. The manufacturer, specific device model, security patches, market variant, carrier, and current device state can significantly influence available forensic possibilities.
The most important message of this evolution is not only that devices have become more secure. More importantly, the relationship between physical access and the actual ability to access data has changed.
In older generations, the device itself was often the starting point of an investigation. In modern devices, it is only one part of a much more complex trust system.
The Security Awakening of the Industry
The change in Android’s security model did not happen overnight, nor was it caused by a single individual technology. It was the result of a broader change in the role smartphones began to play in everyday life.
Because of this, the loss or compromise of a mobile device no longer means only the loss of a physical device. In many cases, it represents a potential loss of access to the user’s entire digital environment.
The industry therefore changed its security priorities. The goal was no longer only to provide users with maximum flexibility and device customization, but to build a platform capable of protecting data even when an attacker physically possesses the device. [7][8]
At the same time, the security environment in which mobile devices operate also changed.
Smartphones became valuable targets for different types of attacks. In addition to traditional threats such as device theft, attempts to bypass protection mechanisms, and malicious applications, high-level attacks emerged, including commercial spyware solutions designed for targeted surveillance of users. Systems such as the Pegasus spyware platform demonstrated that mobile devices are no longer only personal tools, but can represent highly valuable targets for attackers with significant resources. [9][10]
For manufacturers, this meant a change in the fundamental development philosophy.
The question was no longer only:
“How can we give users the greatest possible control over the device?”
but:
“How can we enable the device to determine by itself which code, environment, and access method it can trust?”
This way of thinking created the foundation of the modern Android security model. Trust is no longer only a decision made by the operating system, but the result of cooperation between multiple layers of protection: hardware, firmware, operating system, security modules, and user authentication. [7][11]
For digital forensics, this represents a fundamental change.
In older generations of devices, investigators primarily thought about how to gain access to the system. With modern devices, the question is different:
Can the system allow access to the data in its current security state at all?
This change explains why modern mobile forensics depends less and less only on physical access to the device and increasingly on understanding the security architecture behind it.
Security Moves Below the Operating System
One of the greatest changes in the modern Android security model is the fact that key security decisions are no longer made only within the operating system itself.
In older generations of devices, a significant portion of security mechanisms was implemented through software. If someone managed to compromise the operating system and obtain elevated privileges, there was a possibility of accessing functions that were otherwise restricted.
Modern Android devices are based on a completely different approach.
Security no longer begins when Android starts. It begins much earlier — at the stage when the device is just starting its basic components and deciding which software it can trust.
During device startup, a cryptographic verification chain takes place in which each stage confirms the integrity of the next stage before allowing it to execute. The bootloader verifies the firmware, the firmware verifies the next boot components, and the operating system verifies its own integrity before becoming active.
This concept is known as Android Verified Boot (AVB) and represents one of the foundations of the modern trust model in Android devices. [12]
For forensic investigators, this change is extremely important because it changes the very definition of access to the device.
In the past, the reasoning was often:
If we can obtain a sufficiently high level of system access, we can open the path toward user data.
With modern devices, this assumption is no longer always correct.
It is possible to have a certain level of access to the operating system, service components, or individual device partitions, while the most important evidentiary data remains protected because its cryptographic keys are tied to hardware security mechanisms and the current state of the device. [13][14]
This is exactly why modern mobile forensics must clearly distinguish between two things:
access to the operating system
and
access to user evidentiary data.
These are no longer the same problem.
Security Protection Expands Through Hardware-Backed Mechanisms
Protection is further expanded through the use of hardware-supported security functions.
Modern Android devices use mechanisms such as hardware-backed Keystore, Trusted Execution Environment (TEE), and security elements such as StrongBox, which allow the most sensitive cryptographic materials to be protected outside the main operating system. [13][14]
The idea behind this architecture is relatively simple.
If the key protecting the data exists only inside the main operating system, then compromising that system represents a serious security problem. However, if the key is protected by a separate hardware security mechanism, an attacker no longer needs only to bypass software protection — they must find a way to compromise the entire security chain.
This has become the goal of modern security design for manufacturers.
Data is no longer protected only by the user’s password or by restrictions within Android. It is protected through a combination of user authentication, cryptography, hardware, and the security state of the device.
Ultimately, manufacturers have an interest in selling users the “most secure model on the market.”
This change has a direct impact on the way digital forensics professionals operate.
Today, it is no longer enough to know only the operating system or have a tool capable of communicating with the device. It is necessary to understand the entire security chain: from the moment the device starts, through system integrity verification, all the way to how cryptographic keys are created and used.
This is exactly why two identical devices can represent completely different forensic situations.
One device may be analyzed at a moment when the user has just been using the phone, when the required keys are available and when security mechanisms allow certain operations.
The other device, the same model and the same system version, after a reboot may represent a completely different challenge because protection mechanisms are activated again, and access to data becomes dependent on user authentication and the state of the security system.
For a forensic investigator, this means one very important thing:
The value of a device is no longer determined only by its model, but by the moment when it was discovered and the state in which it exists.
A modern Android device is therefore no longer just a computer with an operating system and storage.
It is a security system in which hardware, firmware, operating system, and cryptography work together to decide when certain data becomes available.
This is why the security of modern smartphones can no longer be understood only by analyzing Android as an operating system.
Security has moved beneath it.
USB: From Practical Feature to Security Boundary
Few technologies illustrate the transformation of the Android security model as clearly as USB connectivity.
For years, USB represented one of the most important connections between Android devices and computers. Through it, users transferred data, developers analyzed applications, service technicians maintained devices, and digital forensic investigators used different communication protocols to collect data.
In earlier generations of Android devices, USB often represented a relatively open interface. If a user enabled USB debugging and authorized a computer, Android Debug Bridge (ADB) could provide valuable access for administration, development, and technical analysis of the device. [15]
For forensic investigators, this is exactly why USB was historically one of the most important starting points of analysis. The physical connection between the device and the computer often represented the first step toward understanding the system, communicating with the device, and using available acquisition methods.
However, the same flexibility that was useful to investigators also represented a security risk.
If an attacker physically obtained a device, a USB connection could represent one possible path for attempting to access data or communicate with the system without the user’s knowledge. Because of this, manufacturers began restricting USB behavior, especially when the device was locked.
Today, modern Android devices generally require explicit user confirmation before allowing sensitive data operations. When the device is locked, the USB connection is often limited to charging, while data transfer and development interfaces remain disabled until the user authenticates the device. [16][17]
At first glance, this change may appear inconvenient for users.
From a security perspective, however, the logic is very clear.
If a user connects a phone to an unknown computer, a public charging station, or a potentially compromised USB device, limiting communication reduces the possibility of unauthorized access or attempts to compromise the device.
An example of such a risk is represented by advanced USB implants such as the O.MG Cable, which demonstrate that a cable is no longer necessarily only a passive piece of electronics used for transferring power and data. In certain cases, it can contain additional electronics capable of performing functions that a user would not expect from ordinary USB accessories. [18]
For the average user, these changes usually remain invisible.
For a digital forensic investigator, they can be critical.
The same physical device can represent completely different investigative situations depending on:
- whether the device is powered on or powered off,
- whether it is unlocked or locked,
- whether it previously authorized a specific computer,
- whether it was rebooted after seizure,
- whether cryptographic keys are still available.
Because of this, USB today is no longer only a communication channel.
It has become part of the device security model.
The change in the USB model clearly demonstrates the broader philosophy of modern mobile security.
In the past, the goal was to provide the device with as many communication and customization possibilities as possible. Today, the device first evaluates whether that communication should be trusted.
For forensic investigators, this represents one of the greatest changes in the way of thinking.
It is no longer enough to have a physical connector and the appropriate tool.
It is necessary to understand under which security conditions the device allows communication.
How digital forensic investigators will communicate with modern mobile devices if manufacturers’ long-standing announcements that they will “remove” USB ports from their flagship devices become reality, only time will tell.
The absence of a USB port is not unknown to digital forensic investigators, because they have certainly encountered thousands of times the situation where a USB port was defective.
Of course, technologies enabling wireless data transfer from mobile devices already exist today, but the question remains what additional security mechanisms manufacturers will implement to ensure that the entire “package” remains secure.
Adding the Security Component “Auto Blocker”
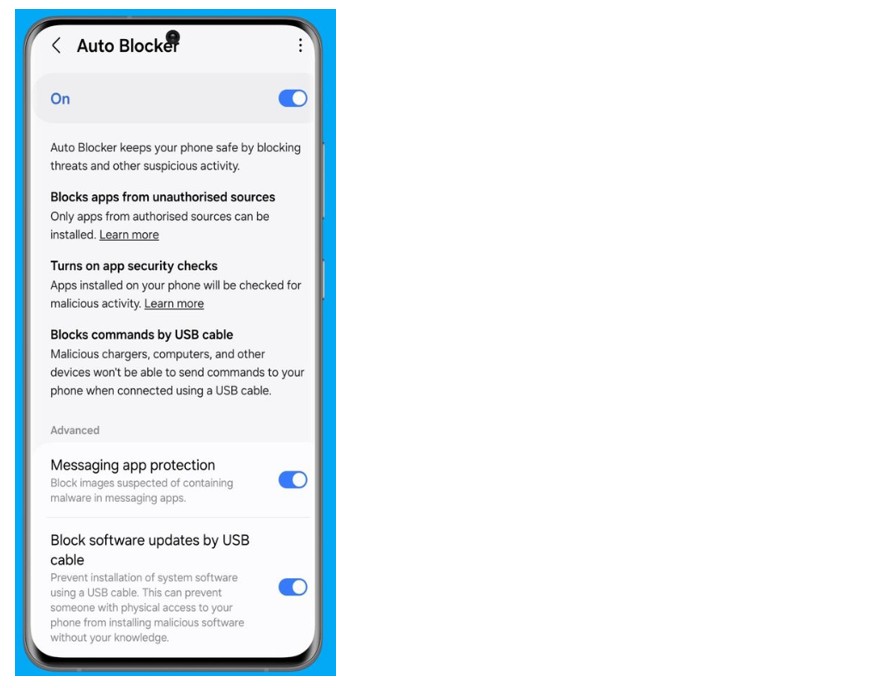
Device State as Part of the Security Model
One of the greatest changes in the modern security model is the fact that a device is no longer only a passive storage container for data.
Older generations of security models primarily focused on protecting content inside the operating system. Access to data mainly depended on who was attempting to access the device and whether they possessed the appropriate credentials.
Modern devices use a more complex approach.
A security decision is no longer tied only to the identity of the user, but also to the integrity of the device itself. Hardware, firmware, operating system, security modules, and cryptographic mechanisms together determine whether a specific function or piece of data can be accessed.
In other words, the device no longer checks only who is requesting access, but also whether the environment from which that request originates is sufficiently trustworthy. [19][20]
This concept represents an important change compared to earlier generations of devices.
In the past, physical possession of the device was often considered the most important prerequisite for analysis. If an investigator had the device in their hands, it was expected that, with appropriate technical knowledge and tools, they would find a way to access the data.
Modern security models change this relationship.
Physical access alone is no longer sufficient. The device actively participates in deciding which capabilities it will enable and under what conditions.
For digital forensics, this means an important change in perspective:
It is not enough to understand where data is located — it is necessary to understand the mechanisms that determine when that data becomes available.
Because of this, a modern smartphone can no longer be viewed only as a storage medium.
It has become a security platform that connects hardware, operating system, user authentication, and connected services.
This change explains why access to the operating system today does not necessarily mean access to evidentiary data.
In modern mobile forensics, one of the most important distinctions becomes:
Access to the device is not the same as access to evidence.
Mobile Security Extends Beyond the Device Itself
Another important consequence of the development of modern security models is the change in how we view the mobile device.
Several years ago, a smartphone was often considered the primary location where a user’s digital traces existed. Photos, messages, contacts, documents, and activity history were mostly associated with the physical storage of the device itself.
Today, such a view is no longer sufficient.
A modern smartphone represents only one part of a broader digital ecosystem that includes cloud services, computers, tablets, wearable devices, applications, and different data synchronization platforms.
User data is no longer necessarily tied to one physical location.
Photos may exist simultaneously on the device and in a cloud service. Documents may automatically synchronize between multiple platforms. Communication applications may use their own infrastructure for storing and transferring data. Authentication mechanisms often connect multiple devices into a single security system.
This change significantly affects the way digital forensics must be approached.
The phone is no longer only a data container.
It is an entry point into the user’s broader digital identity.
Because of this, compromise or analysis of a single device does not necessarily provide a complete picture of user activity. Valuable digital traces may exist in different locations, under different security models, and across different ecosystems.
This means modern analysis can no longer be limited only to the question:
“What can we find on the phone?”
It must also include questions such as:
“Which other services does this device use?”
“Which data is synchronized outside the device?”
“Which other digital traces are connected to the same user identity?”
Cloud as an Extension of the Mobile Device
Cloud services have become an integral part of everyday smartphone usage.
For most users, the boundary between locally stored data and remote services almost no longer exists.
Photos are automatically backed up, contacts are synchronized with user accounts, applications store data on their own servers, and device backups may contain information that is no longer stored locally on the phone.
This change has an important consequence:
Protection and analysis of user data are no longer only a matter of the physical device.
They involve user accounts, authentication mechanisms, access tokens, and security policies of connected services. [21][35]
Because of this, modern security models increasingly include multi-factor authentication, hardware-protected keys, and identity verification mechanisms that extend beyond a single device. [35]
Applications as Separate Security Ecosystems
Another important change relates to the applications themselves.
In the past, the operating system was often considered the primary security environment. If an investigator understood how the system worked, a large portion of user data could be analyzed through its structure.
Today, applications represent separate security entities.
Banking applications, communication platforms, business tools, and authentication applications develop their own security mechanisms, data storage methods, and communication models.
Some information is no longer available only through the device file system, but depends on the security of the application itself, the user account, and the remote infrastructure used by the application.
For modern digital forensics, this represents an important change.
It is not enough to understand only the operating system of the device.
It is necessary to understand the ecosystem of applications used by the user.
A New Perspective on Mobile Security
The development of mobile technologies has changed the fundamental question.
In the past, the common question was:
“Where is the data located?”
Today, it is equally important to ask:
“How is the data connected?”
A user’s data may extend across the phone, cloud services, applications, computers, and other connected devices.
Because of this, modern mobile security no longer protects only one device. It protects the user’s digital identity that is realized through that device.
This is exactly why the future of mobile forensics will not be defined only by the ability to access a phone, but by the ability to understand the entire digital ecosystem represented by that phone.
Samsung’s Security Evolution and Why It Matters
If there is one manufacturer that perhaps best demonstrates the direction in which Android security has evolved, it is Samsung.
Galaxy devices have held a special position in the mobile ecosystem for years. Their widespread use among private users, business organizations, and government institutions has made them one of the most important Android platforms on the market.
At the same time, Samsung has undergone a significant transformation in its security philosophy over the years.
Older generations of Galaxy devices were created during a period when Android strongly emphasized openness, development, and customization possibilities. Various service modes, development tools, and software modification capabilities represented an important part of the Android ecosystem at that time.
For advanced users, technical specialists, and digital forensic investigators, this approach provided a greater level of control over the device and often opened additional possibilities for technical analysis.
However, as smartphones became increasingly important carriers of personal, business, and authentication data, Samsung gradually changed its approach. The device was no longer viewed only as a platform controlled by the user, but as a security system that must protect data even when physical access to the device exists.
This change is visible throughout Samsung’s security ecosystem.
Components that once primarily served development, servicing, and device customization gradually gained a new security role. The bootloader, recovery, and different service modes are no longer only technical tools for managing the device, but elements of a broader trust chain that determines whether the device can trust the software being executed and the environment in which it operates.
This is exactly why Samsung represents a very good example of the change that occurred throughout the entire mobile industry.
Functions that once provided users with greater freedom have today become part of a security model that defines the boundaries of permitted modifications.
For digital forensics, this evolution has particular importance.
With older devices, analysis possibilities often depended more on the investigator’s technical knowledge and available service channels. With modern Samsung devices, the result of analysis increasingly depends on how the device’s security model was designed and which possibilities that model allows.
Because of this, two devices of the same model no longer necessarily represent the same forensic situation.
The difference is not only in the hardware or software version, but in the security architecture that determines which access methods are possible.
Knox – From Business Protection to the Foundation of Security Architecture
When Samsung introduced Knox, many initially associated it primarily with business users and mobile device management.
Enterprise users used Knox to separate business and personal data, apply security policies, and manage large numbers of devices.
However, modern Knox represents much more than a business add-on. It has become a fundamental part of Samsung’s security architecture, connecting hardware, firmware, and the operating system.
Knox includes various security mechanisms, including system integrity verification, protection of sensitive data, security policies, and hardware-supported security functions. [25]
The most important change is not only in individual features, but in the overall way of thinking. Security is no longer an additional layer enabled after the device has been created, but is built directly into the core architecture of the platform.
For forensic investigators, this difference is particularly important.
A modern Samsung device is not simply an Android phone with additional security features. It is a platform in which hardware, firmware, operating system, and security mechanisms collectively define the boundaries of access.
This is why understanding the Samsung Knox ecosystem is not important only for administrators and business users. It has become part of understanding modern mobile forensics.
Bootloader, Download Mode, and Recovery Mode – From Tools of Flexibility to Security Control Points
One of the best examples of Samsung’s security evolution can be seen through components that once represented symbols of Android platform openness: the bootloader, Download Mode, and Recovery Mode.
In earlier generations of Android devices, these functions were primarily associated with development, servicing, and device customization possibilities. For advanced users, developers, and technical specialists, they represented a way to gain deeper understanding and control over the device.
Today, their role looks completely different.
The same components have become part of the security trust chain that determines what can be executed, modified, or restored on the device.
Bootloader – From Symbol of Openness to Security Control Point
The bootloader is a component that runs before the operating system and plays a key role in the device startup process.
Its primary task is to verify which software components will be loaded and allow startup to continue only if they meet defined security requirements.
In the earlier Android ecosystem, unlocking the bootloader often represented an important possibility for users who wanted greater control over their devices. Installing custom systems, developing alternative software, and exploring device behavior were part of the broader philosophy of platform openness.
Over time, its role changed.
Modern devices use cryptographic integrity verification mechanisms that ensure only trusted software is executed during startup. Any modification of critical system components must pass security checks, and attempts to bypass protection may result in changes to the security state of the device. [24][26]
On Samsung devices, bootloader unlocking possibilities depend on the model, market, and device version. However, the overall direction of the industry is clear:
The startup process is no longer only a technical function, but one of the most important security control points of the device.
For digital forensics, this means that the ability to modify or access lower system layers is no longer only a technical issue. It is connected to the entire security model of the device.
Download Mode – From Service Mode to a Controlled Security Function
Samsung’s Download Mode represents another good example of this transformation.
For years, Download Mode was one of the most recognizable service environments on Galaxy devices. It was used for installing official firmware, maintaining devices, and performing system recovery procedures.
In the context of earlier device generations, it represented an important service channel that allowed technical users deep control over the device.
However, modern devices no longer allow such operations without additional verification.
The firmware installation process today includes digital signature verification, system integrity protection, and mechanisms that prevent the use of unauthorized or older software versions that could represent a security risk. [24][27]
One important element of this approach is anti-rollback protection.
Its purpose is not only to prevent technical downgrading to older versions of software, but also to protect the device from reintroducing known security vulnerabilities.
Through this, Download Mode stops being only a service tool and becomes part of the security model that controls which changes the device accepts as legitimate.
Samsung also changes this behavior from version to version and continues to “strengthen” security, increasingly limiting and preventing users from using the same functions without additional verification.
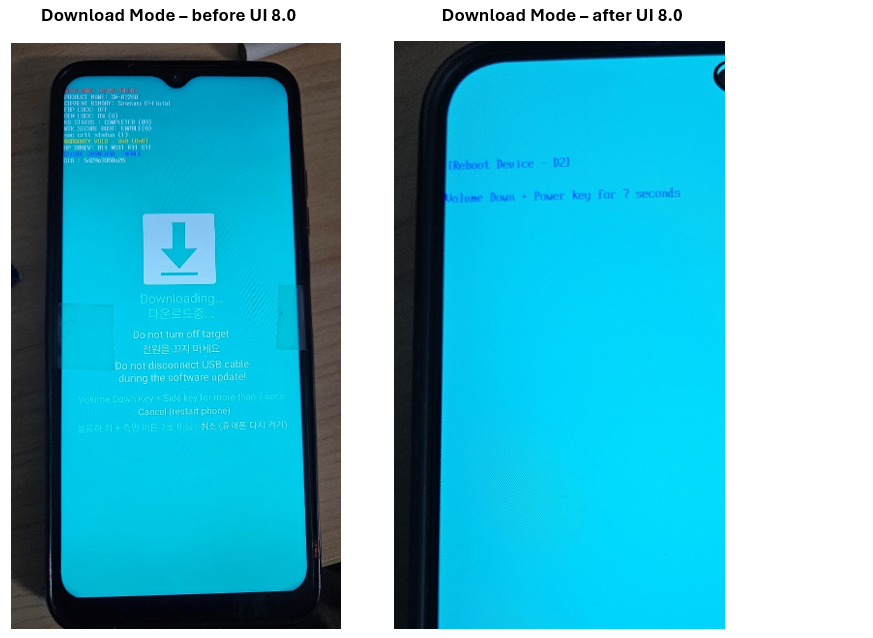
Recovery Mode – Service Environment Within the Security Model
Recovery Mode has undergone a similar transformation.
On older devices, recovery environments were often viewed as service tools for repairing, updating, and maintaining the system. Because of their flexibility, they became an important part of the Android development community.
Today, recovery is no longer an isolated service environment.
It is part of the device security architecture, and all operations performed through it are subject to integrity verification and rules designed to protect user data. [23][24]
Every device component must simultaneously enable legitimate maintenance while preventing abuse.
What Does This Change Mean for Digital Forensics?
For forensic investigators, the most important consequence of this evolution is the change in the way of thinking.
In the past, bootloader, service modes, and recovery environments often represented possible paths toward deeper device analysis.
Today, they are primarily part of the security mechanism that defines the boundaries of access.
This does not mean they have become irrelevant.
Quite the opposite.
Understanding how they work has become even more important, because without understanding the device’s security chain, it is impossible to properly evaluate which analysis methods are possible, which are limited, and why a certain access method works or does not work.
Samsung’s evolution is therefore not only a story about devices becoming more closed.
It is an example of a broader transformation in which former tools of openness have become foundations of security.
As with Download Mode, Samsung has also limited the capabilities of Recovery Mode with newer system versions, disabling many of the possibilities that this option previously provided.
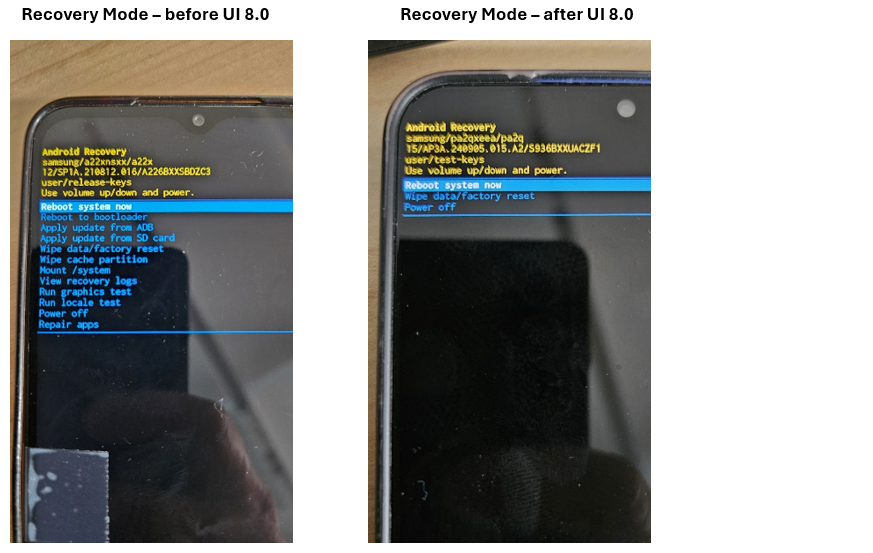
The Rest of the Android Ecosystem: Different Manufacturers, the Same Security Direction
Although Samsung represents one of the most visible examples of Android security evolution, the transformation of the security model is not limited to a single manufacturer.
Almost the entire Android ecosystem is undergoing a similar transformation.
Differences between manufacturers still exist. Some maintain a greater level of openness toward developers, some more strongly control system modifications, while others build their own security ecosystems that go beyond the traditional Android model.
However, the common direction is very clear.
The mobile industry is moving away from a model in which physical access to the device represented the starting point of analysis, and toward a model in which security is determined by cryptographic verification, hardware protection, and trust relationships between different parts of the system.
A modern smartphone is no longer only a device that executes user commands.
It is a security platform that continuously evaluates the integrity of its own environment.
Google Pixel – Openness Combined With Strong Hardware Protection
Google Pixel devices occupy a special place within the Android ecosystem because they represent the most direct implementation of Google’s vision for the platform.
Unlike many manufacturers that significantly modify Android according to their own requirements, the Pixel line has traditionally attracted developers, security researchers, and users who want a more direct relationship with the Android platform.
What makes Pixel devices interesting is the combination of relative openness and a very strong security model.
The ability to officially unlock the bootloader, access development tools, and obtain platform information does not mean the device is less secure. On the contrary, Google built Pixel’s security architecture around hardware protection, cryptographic verification, and protection of sensitive operations.
One of the key elements of this approach is the Titan security processor, which participates in protecting cryptographic keys, verifying device integrity, and providing platform security functions. [29]
Pixel demonstrates an important lesson in modern mobile security:
Openness and security are no longer necessarily opposing concepts.
True security is no longer determined only by how many capabilities are available to the user, but by how the fundamental security mechanisms are designed.
GrapheneOS – Security Through a Different Philosophy
A particularly interesting example within the Pixel ecosystem is GrapheneOS.
Unlike manufacturer-specific Android modifications, GrapheneOS represents an attempt to build an additionally hardened security environment based on the Android platform.
Its approach demonstrates that mobile system security is not defined only by manufacturer hardware, but also by the way the operating system, application model, and security policies are designed.
This example is important because it demonstrates a broader industry change:
Security is no longer only a device feature, but the result of a combination of hardware, software, and configuration. [30]
Xiaomi, OnePlus, and Other Manufacturers – The End of the Era of Complete Openness
Xiaomi and OnePlus represent an interesting example of the transformation that occurred among manufacturers whose popularity was partly built on enthusiast communities.
Xiaomi was long known for a large user community, development of alternative software, and greater openness toward device modifications. Similarly, OnePlus built its early identity among users who appreciated the ability to modify and explore the system.
However, as smartphones became increasingly important for financial applications, business communication, digital certificates, and authentication, industry priorities changed.
Openness is no longer the only quality criterion.
Modern devices must ensure system integrity, protect sensitive data, and satisfy the requirements of applications that depend on a secure environment.
Because of this, these manufacturers have also gradually introduced stricter bootloader controls, security verification, and system integrity protection. [31]
This change clearly demonstrates a broader trend:
What once represented an advantage for advanced users can today represent a security risk in everyday use.
Huawei – A Different Path Toward Ecosystem Control
Huawei represents a somewhat different example due to the development of its own ecosystem and transition toward the HarmonyOS platform.
Unlike manufacturers that remain within the traditional Android model, Huawei has increasingly developed its own approach to operating systems, services, and security architecture in recent years.
This development demonstrates another important characteristic of modern mobile security:
Security is no longer viewed only through the device itself, but through the entire relationship between hardware, operating system, applications, and cloud infrastructure. [32]
Common conclusion of the Android ecosystem
When comparing Samsung, Google, Xiaomi, OnePlus, Huawei, and other major manufacturers, it becomes clear that there is not only one security model.
Some manufacturers emphasize openness, some emphasize control, while others focus on complete integration of their own ecosystem.
However, the fundamental direction is the same.
Mobile devices are becoming less like ordinary computing devices and more like security platforms that determine themselves which components, code, and environments they can trust.
For digital forensics, this means an important change in perspective.
It is no longer sufficient to know only the device model or available tools, but it is necessary to understand the manufacturer’s security philosophy, device architecture, and the way a particular ecosystem defines access boundaries.
A new perspective on modern mobile security
The development of mobile security models has changed the way we must look at smartphones.
The most important change is not found in individual technologies or specific protection mechanisms, but in the fact that understanding a modern device is no longer possible without understanding the entire system in which it exists.
For digital forensics, this means that analysis can no longer be based only on knowledge of a specific device model or available extraction methods.
It is necessary to understand the principles on which modern platforms are built, the way manufacturers develop security mechanisms, and how these changes affect analytical possibilities.
Because of this, the greatest value of an expert is no longer only in knowing current tools, but in the ability to understand technology that is constantly changing.
Continuous education as the key to expertise
The greatest challenge of modern mobile forensics may not be only the complexity of technology, but the speed at which it develops.
A few years ago, it was possible to study a specific device model in detail, understand its architecture, and use that knowledge for a relatively long period of time.
Today, the situation has changed significantly.
New generations of devices, new operating system versions, security patches, changes in hardware architecture, and new methods of data protection continuously reshape the field of mobile forensics.
A method that is effective today may tomorrow become limited by a change in a single security component, a new system version, or a different implementation approach by the manufacturer.
Therefore, digital forensics is not an area where knowledge can be acquired once and then simply applied for years.
Knowledge must be continuously renewed.
This includes monitoring manufacturer technical documentation, security research, development of new technologies, changes in operating systems, and experiences of the entire professional community.
Equally important are practical testing of new devices, analysis of new system versions, and regular professional training that enables understanding of new approaches before they become everyday challenges in the laboratory.
As I often emphasize during training:
“A digital forensic examiner must be an enthusiast.”
Not because simply loving technology is enough, but because without a genuine desire for learning, research, and following changes, it is not possible to keep up with the development of the field over the long term.
An expert who only knows the tool may be limited by the changes that come.
An expert who understands the technology behind the tool can adapt to new challenges.
The future of mobile forensics
If current trends continue, the future of mobile forensics will not be defined only by the ability to access an individual device.
It will be defined by the ability to understand the entire technological environment that the device represents.
This requires a combination of different areas of knowledge:
- device security architectures,
- operating systems,
- hardware protection mechanisms,
- application platforms,
- the way manufacturers develop their ecosystems.
But above all, it requires a willingness for continuous learning.
Mobile forensics is not an area that has a final point of knowledge.
Each new generation of devices brings new challenges, but also new opportunities for those who understand them.
Therefore, the most valuable experts of the future will be those who do not only follow tools, but understand the technology behind them.
Conclusion: A new era of mobile forensics
Android devices have not become more complex to analyze because manufacturers’ goal was to make the work of investigators more difficult, but because these devices have become one of the most important places where a user’s digital identity exists.
As we say in our professional jargon:
“I have their entire life in my hands.”
Generally, when reviewing the obtained data, it is possible to create a profile of the device user, from everyday activities and behavioral patterns to potentially discovering a double life or a divided personality.
Because of this, modern mobile forensics can no longer be based only on finding ways to access data.
The most important question is no longer only:
“How do we get to the data?”
but:
“Why does the device consider a certain type of access trustworthy or untrustworthy?”
Understanding the answer to this question becomes the foundation of the work of a modern digital forensic examiner.
A few years ago, the greatest value often came from knowing specific extraction methods, service procedures, and capabilities of individual devices.
Today, the situation is different.
The value of an expert increasingly comes from the ability to understand security architecture, platform behavior, and the reasons why a specific method works or does not work.
Tools will change, manufacturers will introduce new security mechanisms, operating systems will evolve, and analytical methods will constantly need to adapt.
But fundamental knowledge of how technology works remains the most important advantage.
The development of mobile security will never be complete
Manufacturers will continue improving device protection, developing new security architectures, and introducing new ways of protecting user data.
At the same time, digital forensics will continue to evolve.
Investigators, security experts, and forensic tool manufacturers will have to continuously adapt to new technologies and new challenges.
This is not a conflict in which one side eventually wins, but a continuous development in which security and analysis shape each other.
The most important factor, however, remains the human being
Regardless of how advanced devices become and how sophisticated the available tools are, the final result always depends on the knowledge of the person using them.
An expert who understands only the tool may be limited as soon as technology changes.
An expert who understands security principles, system architecture, and industry development will be able to adapt to new generations of devices.
Therefore, continuous learning, research, and monitoring technological changes are not an additional value in digital forensics.
They are its foundation.
Final thought
Android devices have not lost their openness because technology has moved backward.
They have become more closed in certain areas because they have become more secure, more complex, and more important than ever before.
The challenge of modern mobile forensics is not only finding a way to access data, but the real challenge is understanding the security model that determines when, how, and under what conditions that data can become available.
Because in the world of modern mobile technology, the greatest change is not only that devices protect data better today.
The greatest change is that devices are no longer passive containers of information.
Understanding that trust relationship has become one of the most important skills of modern digital forensics.
Author:
Saša Deković
Digital Forensics Consultant
Resources
[1] Android Open Source Project (AOSP) – Android Security Documentation
https://source.android.com/docs/security
[2] Android Open Source Project (AOSP) – Android Verified Boot (AVB)
https://source.android.com/docs/security/features/verifiedboot
[3] Android Open Source Project (AOSP) – File-Based Encryption
https://source.android.com/docs/security/features/encryption/file-based
[4] Android Open Source Project (AOSP) – Hardware-backed Keystore
https://source.android.com/docs/security/features/keystore
[5] Android Open Source Project (AOSP) – StrongBox Keymaster
https://source.android.com/docs/security/features/keystore#strongbox
[6] Android Developers – Android Debug Bridge (ADB)
https://developer.android.com/tools/adb
[7] Android Open Source Project (AOSP) – USB Architecture
https://source.android.com/docs/core/connectivity/usb
[8] Android Security Bulletins
https://source.android.com/docs/security/bulletin
[9] Google Threat Analysis Group
https://blog.google/threat-analysis-group/
[10] Amnesty International Security Lab – Technology Research
https://www.amnesty.org/en/tech/
[11] Samsung Knox Security Documentation
[12] Samsung Knox Platform Security
https://www.samsungknox.com/en/security
[13] Samsung Knox Vault Documentation
https://docs.samsungknox.com/admin/fundamentals/knox-vault/
[14] Google Pixel Security Overview – Titan Security
https://security.googleblog.com/
[15] GrapheneOS Documentation
[16] Xiaomi Security Center
[17] Huawei Cyber Security and Privacy Protection
https://www.huawei.com/en/trust-center
[18] O.MG Cable – Hak5 Security Research
https://shop.hak5.org/products/omg-cable
[19] NIST Mobile Device Security Guidelines
https://csrc.nist.gov/publications
[20] Google Safety Center – Account and Device Security
[21] Android Open Source Project (AOSP) – Security Architecture
https://source.android.com/docs/security/overview
[22] Android Open Source Project (AOSP) – Authentication and Device Protection
https://source.android.com/docs/security/features/authentication
[23] Samsung Knox Platform Security White Paper
https://docs.samsungknox.com/admin/fundamentals/security-white-paper/
[24] Android Open Source Project (AOSP) – Rollback Protection
https://source.android.com/docs/security/features/verifiedboot/verified-boot
[25] OPPO Security Documentation
[26] NIST Cybersecurity and Mobile Device Protection Resources